

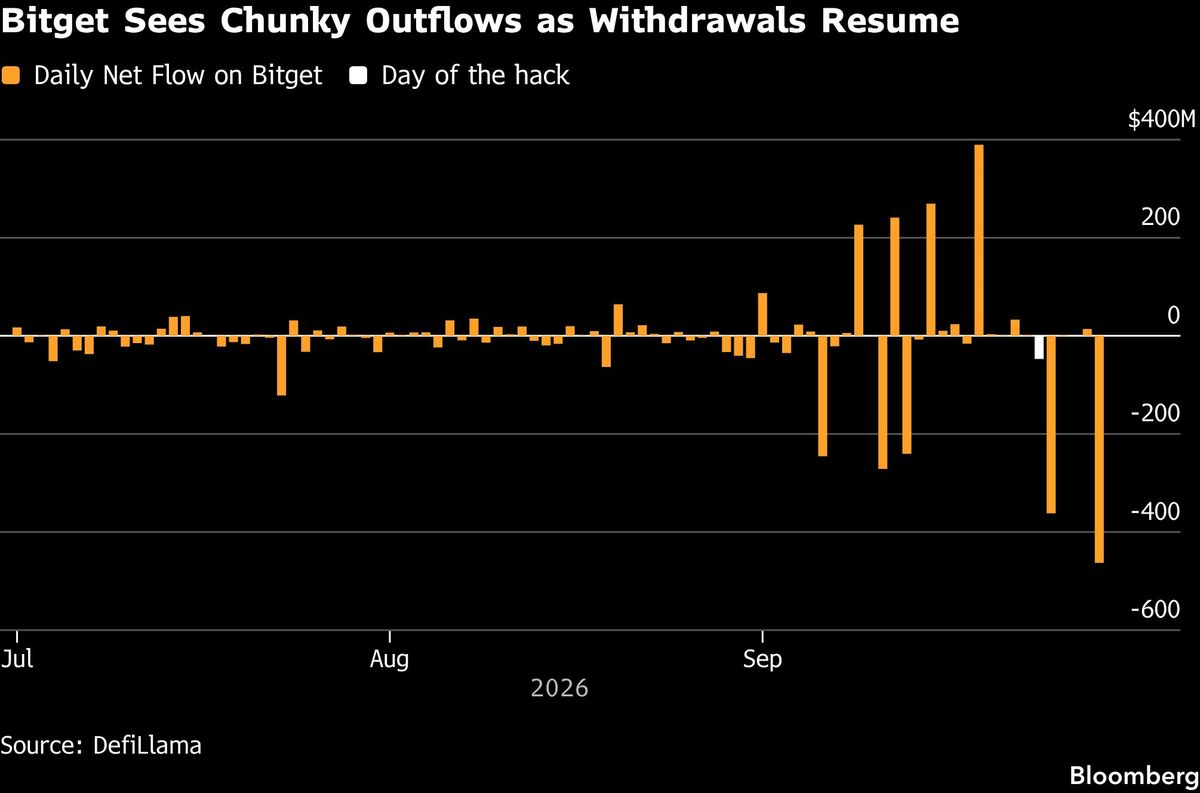
(Sept 29): Hacked crypto exchange Bitget recorded roughly US$463 million (RM1.89 billion) in net outflows in the 24 hours into Tuesday as customers moved assets off the platform following last week’s US$388 million theft.
The surge came after Bitget began restoring withdrawals and marked the largest one-day net outflow since data aggregator DefiLlama began tracking proof-of-reserves four years ago. The exchange currently holds about US$5.7 billion in reserves.
Bitget is reopening withdrawals in stages, starting with bitcoin on Monday, followed by ether and USDT. Withdrawals of other tokens, along with fiat and peer-to-peer services, are set to resume Oct 2, Bitget said in a post on its website. The staggered rollout was a security measure “unrelated to the sufficiency or availability of user assets,” the company said.
The exodus is another blow to the exchange — among the world’s top 10 by trading volume — as it seeks to recover from a hack that cybersecurity experts have said was likely linked to North Korea. Tuesday’s outflows represent more than 10% of its current reserves.
The US$464 million user protection fund Bitget had cited to assure customers their funds were safe has now fallen below US$200 million, according to the three wallet addresses that Bitget cites as the source of the funds.
“The Protection Fund is being used to absorb the financial impact of the incident,” Bitget CEO Gracy Chen said in an emailed response to Bloomberg. “Bitget will replenish the fund using its own capital, with the fund targeted to be above US$300 million within one week.”
The timeline
Chen said she “immediately got involved with the team” after waking up around the time of the hack at 2.30am in Singapore (same time as Malaysia).
The attacker exploited a vulnerability in a security product supplied by a third party to obtain internal credentials, which were used to send fraudulent withdrawal commands to Bitget’s wallet system, according to Chen. Those commands bypassed existing risk controls, resulting in abnormal transfers.
The breach was confined to portions of hot-wallet and warm-wallet infrastructure, according to Chen. A subsequent investigation found that no private keys or cold wallets were compromised, she added. Hot wallets stay online for frequent transactions, cold wallets stay offline for maximum security while warm wallets sit in between.
The investigation
In addition to working to replenish the funds, the exchange is working with Google’s Mandiant and blockchain-security firm SlowMist to continue to investigate the hack.
While Chen initially pointed to signs of North Korean involvement, a link that outside researchers have now also made, she was cautious about making a final conclusion at this stage.
“What I shared previously was based on preliminary indicators identified during the investigation,” she said. “Those indicators are still being assessed and should not be treated as a definitive attribution.”
Uploaded by Arion Yeow